Credential Leakage


Relevant Teams


Offered through CyberBlindspot
Early Visibility into
Exposed Credentials
CTM360 helps security teams identify exposed credentials linked to their organization and prioritize action to reduce the risk of account compromise. Validated findings and contextual alerts support investigation and response, helping teams reset passwords, revoke access tokens, and secure affected accounts.
How CyberBlindspot Detects and helps Prevent Corporate Credential Leakage
Credential Exposure Monitoring
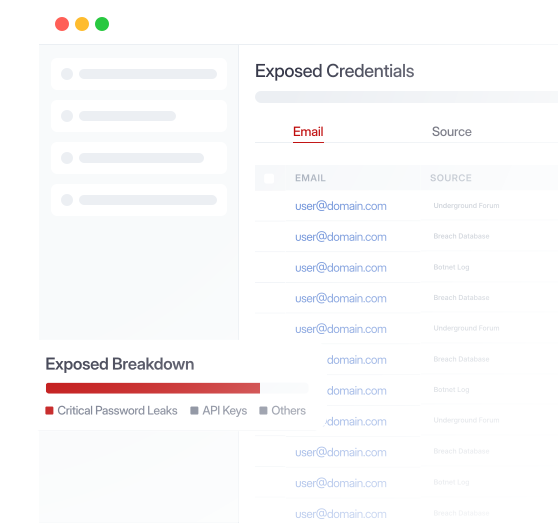
CTM360 provides timely visibility into leaked credentials by continuously monitoring breach databases, malware logs, underground forums, Telegram channels, and other external attack surfaces. The platform detects and validates exposed usernames, passwords, API keys, access tokens, and authentication secrets associated with the organization.
Credential Alerts & Response
CTM360 raises tickets and alerts for detected credential leaks, with details on the exposed credentials and breach source where available. This gives security teams the context needed to investigate the exposure, assess the risk, and prioritize response.
Frequently Asked Questions
How does CTM360 detect leaked credentials and data?
Through continuous monitoring of breach databases, malware logs, underground forums, Telegram channels, GitHub, and cloud storage platforms. Credentials, keys, and sensitive identifiers linked to your organization are flagged promptly.
What happens after a credential leak is detected?
CTM360 tickets and alerts on the relevant finding, providing context to support investigation and prioritization. Security teams can then take appropriate action, such as resetting credentials, revoking tokens, suspending accounts, or escalating the case for further review.