


Defending Against The Next Generation of Digital Attacks
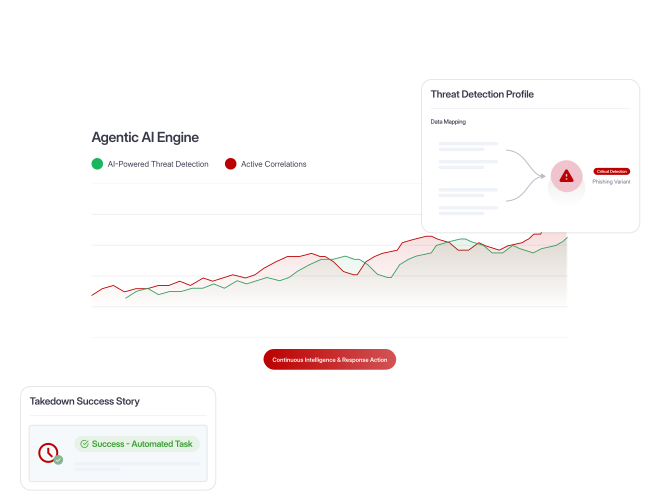

AI-Powered Attacks Operate in Nanoseconds. Security Teams Must Respond at the Same Pace
As an early adopter of artificial intelligence in cybersecurity, CTM360 has embedded Agentic AI capabilities into its workflows to address the growing scale, volume, and complexity of
next-generation cyberattacks.
These capabilities help detect phishing, impersonation, fraud, and malicious infrastructure at scale, enabling security teams to respond faster and stay ahead of increasingly complex threats.
Agentic Threat Intelligence
Leveraging coordinated AI agents and agentic workflows, CTM360 identifies patterns, anticipates emerging threats, and enables proactive action before significant impact occurs. The model is built around four core themes designed to shorten the cycle between observation, understanding, decision-making, and action.
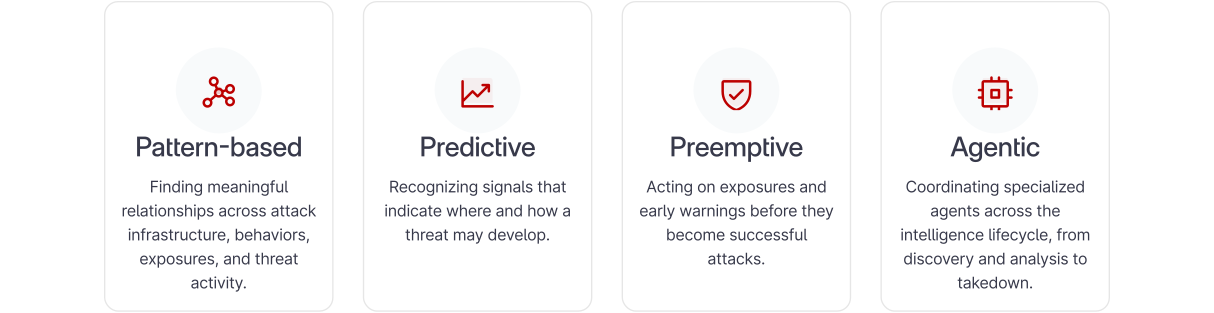
From Individual Indicators to Meaningful Patterns
Threat intelligence is not just about collecting more indicators. It is about connecting individual signals to uncover meaningful patterns, understand their relevance to an organization, and identify potential threats before they materialize.
Leveraging Agentic Workflows, CTM360 continuously evaluates these relationships by comparing new observations with historical intelligence, known behaviors, and the organization’s external context to uncover emerging risks.
Accelerating Security Operations with Agentic AI
Asset Classification for Enhanced EASM
Automatically classifies assets and adds rich context context to discovered assets, helping security teams prioritize risk more effectively.
Image Similarity Detection
Detects visual brand abuse across websites, advertisements, and digital channels, even when logos or branded images have been modified.
Automated Threat Correlation
Connects related signals across assets, infrastructure, campaigns, and threat indicators to reveal hidden relationships and show how attacks are connected and evolving.
Contextual Data Analysis and Enrichment
Enriches threat and digital risk findings with context from multiple intelligence sources, making complex findings easier to understand.
Takedown Reporting and Case Follow-Up
Enables faster and at-scale takedowns and threat disruption with intelligent workflows and Integrated APIs.
Enabling Faster, Scalable Security Operations

Comprehensive Coverage

Agentic AI at Every Step
decision support.

Operational Excellence

Operate at a Scale
greater speed.

Faster Impact
risk reduction