CTEM (Continuous Threat Exposure Management)

Operationalize External CTEM with CTM360
a graphic showing the features
hero background graphics

Operationalize External CTEM with CTM360

Enable CTEM as a continuous security process that connects external exposure, threat intelligence, validation, and response across the
organization’s digital ecosystem.
‍
CTM360 operationalizes Continuous Threat Exposure Management (CTEM) through a layered technology stack that continuously connects external visibility, threat intelligence, validation, and incident response. CTM360 applies CTEM across the wider external threat landscape, starting with understanding the organization’s digital footprint and exposures, then identifying emerging threats and third-party risks, prioritizing what matters most, validating whether risks are genuine or actionable, and finally enabling remediation, investigation, or threat disruption. 

CTEM Stages
CTM360 Capability
Define Your External Exposure Scope
CTM360's pre-populated and pre-configured platform, Hackerview, automatically discovers and maps an organization's internet-facing assets, including domains, subdomains, SSL certificates, IP addresses, and associated technologies, defining the scope of potential exposure and threat targets.
Continuously Discover Exposures & Emerging Threats
HackerView continuously identifies vulnerabilities, misconfigurations, and exposure points through passive and non-intrusive checks across the external attack surface, while CyberBlindspot detects emerging threats such as phishing campaigns, impersonation attempts, malicious domains, and credential leaks targeting the organization.
Prioritize the Risks That Matter Most
Identified exposures and threats are prioritized using a severity-based risk-scoring model that incorporates threat context and exploitability, enabling organizations to focus remediation efforts on the most critical risks & threats affecting their digital environment and third-party ecosystem.
Validate Genuine & Actionable Risk
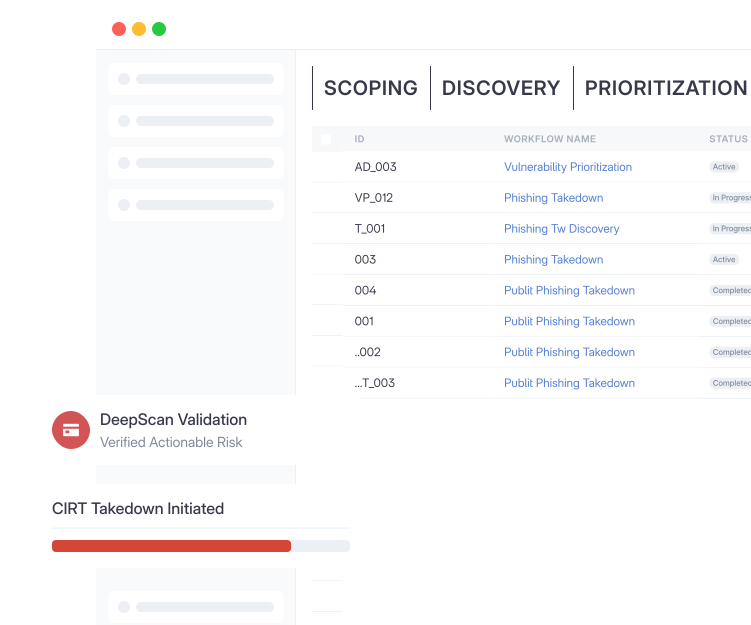
CTM360's DeepScan capability validates exposures through active but non-intrusive checks, including testing for critical vulnerabilities, emerging CVEs, and in-the-wild exploits affecting internet-facing assets. On the other hand, CyberBlindspot analyzes detected threats by examining malicious infrastructure and artifacts (e.g., phishing URLs/pages, look-alike domains, impersonation assets, and credential leaks). The platform then validates the incident's malicious nature, assesses its impact, and determines whether the threat is active and actionable before initiating a response.
Mobilize Response & Threat Disruption
CTM360 supports remediation of external exposures by providing actionable guidance to address vulnerabilities, misconfigurations, exposed services, and other internet-facing risks. In addition, CTM360's Cyber Incident Response Team (CIRT) provides 24/7 managed response, executing takedowns of active threats such as phishing domains, malicious websites, fraudulent social media accounts, and other attacker infrastructure targeting the organization.

Operational Model meets CTI Stack

Discover CTM360 Digital Risk Protection Technology Stack

Request Demo