


External Attack Surface Management


Offered Through HackerView

Get Day One Value Without Configurations or Installations
Provides immediate visibility into your organization’s external security posture without requiring any installation
or configuration.

Automated Digital Assets Inventory (Known, unknown, and shadow IT assets)
Automatically discovers, maps, and maintains an inventory of your organization’s known, unknown, and shadow IT assets across cyberspace. HackerView provides a centralized, graphical view of your external attack surface to help maintain continuous visibility across your digital footprint.

Identify Issues and Indicators of Exposure
Identifies externally visible issues and Indicators of Exposure (IoE) across your digital assets that could serve as potential entry points for attackers. By highlighting exposed services, vulnerable technologies, misconfigurations, and other weaknesses, security teams can address exposures before attackers exploit them.

Comprehensive Visibility of Your Digital Footprint
Provides comprehensive visibility across your external attack surface by combining technical data points such as domains, subdomains, hosts, IP addresses, services, technologies, and SSL certificates with business context such as subsidiaries, executives, social media presence, and other
organizational identifiers.
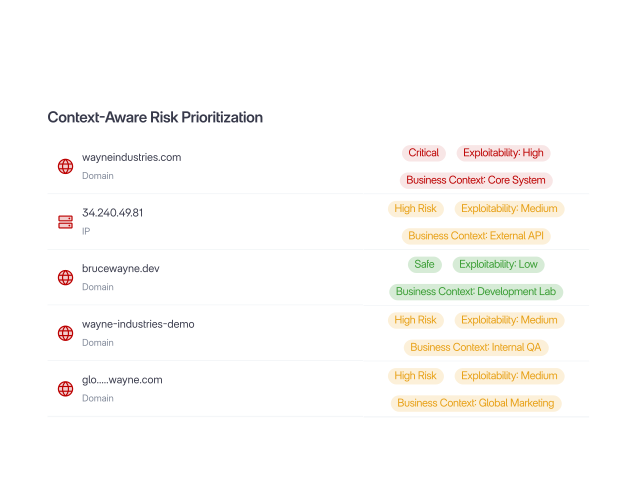
Context-Aware Risk Prioritization
Not every asset or exposure carries the same level of risk. HackerView adds context to discovered assets and identified exposures, enabling security teams to prioritize based on severity, exploitability, asset relevance, business context, and asset criticality.
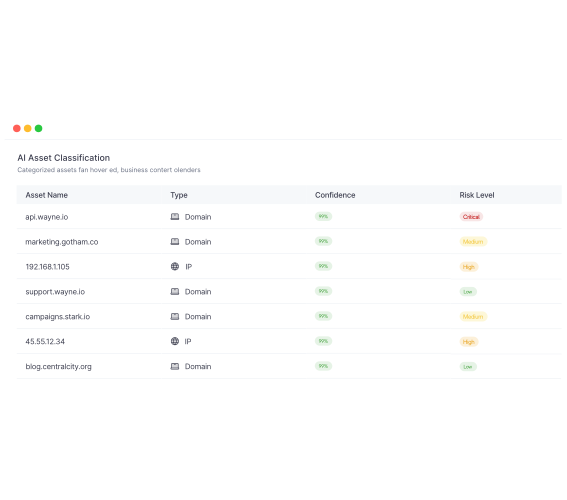
AI-Powered Asset Classification
HackerView uses AI-powered asset classification to add deeper context to your external attack surface. This helps security teams identify critical assets faster, prioritize risk, and focus on the exposures that matter most.
Solutions by HackerView

Issue Management

Security Rating Services

DeepScan - External Exposure Management
Frequently Asked Questions
What is External Attack Surface Management?
External Attack Surface Management (EASM) is the process of continuously identifying, monitoring, and securing an organization's externally facing or publicly accessible assets. This process enables organizations to address weaknesses, misconfigurations, and potential entry points that adversaries could exploit to gain unauthorized access or cause harm.
What are shadow IT or rogue assets, and how does Hackerview help identify them?
Shadow or rogue assets are externally facing assets created without proper security oversight or in violation of the company-defined conventions. Often created by employees, brand teams, or other business units.
Examples include:
- Forgotten or abandoned domains and subdomains
- Test, staging, or development servers exposed to the internet
- Unapproved cloud instances, storage buckets, or SaaS tools
- Visibility on exposed and misconfigured APIs created for testing or integrations
As organizations grow digitally, keeping track of and continuously monitoring all owned External Assets becomes cumbersome.
CTM360 addresses this challenge by consolidating an inventoried catalog of all external-facing assets, preconfigured without requiring end-user input, helping organizations maintain full visibility and control over their digital assets.
What visibility would I gain from EASM?
CTM360’s asset discovery process is designed to help organizations keep track of all their internet-facing digital assets. With detailed categories for domains, IP addresses, hosts, websites, etc., EASM enables a clear and comprehensive inventory, helping you understand your online presence and attack surface.
What pivoting points does Hackerview or CTM360 utilize?
The platform can pivot across various data sources, including WHOIS Records, Reverse WHOIS records, DNS Entries, SSL Certificates, and more.