Microsoft Mandates DMARC for Bulk Email by May2025

What’s on this page
Overview
The fight against email-based threats is intensifying. Following the lead of Google and Yahoo, Microsoft has officially announced the mandatory implementation of email authentication protocols, SPF, DKIM, and DMARC, for high-volume email senders, effective May 5, 2025. Domains sending over 5,000 daily emails to Microsoft's platforms, including Outlook.com, Hotmail.com, and Live.com, will be required to authenticate their messages. Initially, non-compliant messages will be redirected to recipients' Junk folders, with eventual total rejection expected if compliance isn't achieved. This enforcement represents a critical step in securing global email communications from spoofing and phishing threats (Microsoft Tech Community).
Understanding Email Authentication
Email authentication has become essential in combating increasingly sophisticated phishing and spoofing attacks. Three core standards have been adopted widely:
- Sender Policy Framework (SPF: RFC 7208): Verifies the legitimacy of the sending mail server, ensuring messages originate from authorized infrastructure. SPF helps prevent sender address forgery by defining authorized sending sources in DNS records.

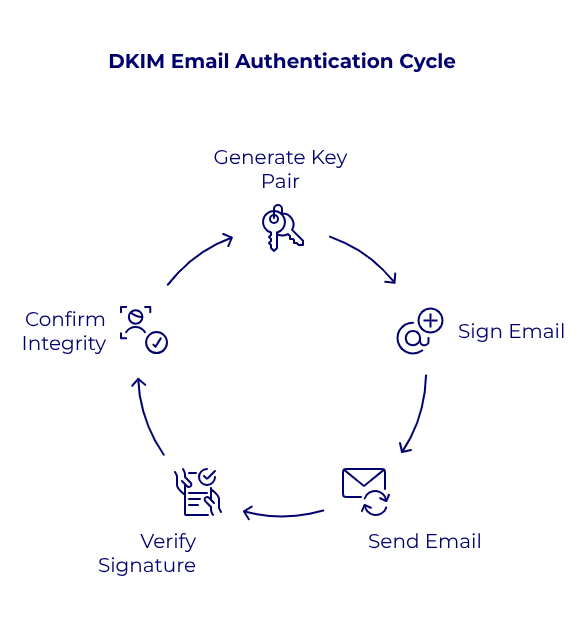
- DomainKeys Identified Mail (DKIM: RFC 6376): Cryptographically signs email messages, allowing recipients to confirm message content hasn't been altered in transit. DKIM leverages public-private key pairs to ensure message integrity and authenticity.
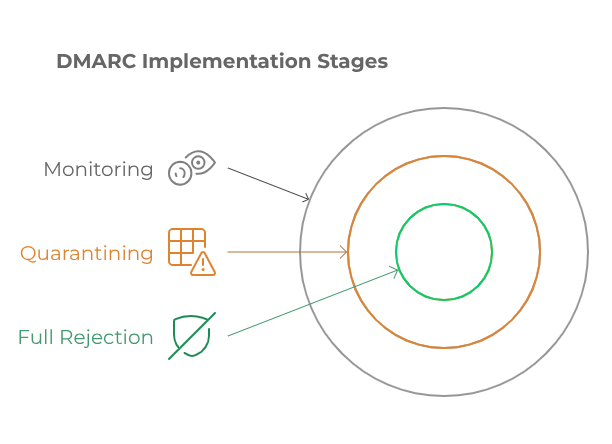
- Domain-based Message Authentication, Reporting, and Conformance (DMARC: RFC 7489): Combines SPF and DKIM to enforce domain alignment, verify authenticity, and provide reporting mechanisms for senders to track email usage and potential abuse. DMARC is recommended to be implemented in three incremental stages: initial monitoring (p=none), intermediate quarantining of suspicious messages to test the policy impact (p=quarantine), and full rejection of unauthorized emails to achieve DMARC compliance (p=reject).
Email Content and Delivery Best Practice Guidance
To help the email ecosystem thrive and ensure that legitimate communications reach users' inboxes, major providers like Google, Yahoo, and Microsoft have released a unified set of technical and content-based requirements. This section consolidates these guidelines into a single resource for senders seeking to avoid spam filtering and maintain high deliverability rates.
1. Message Headers & Structural Integrity
2. Content Hygiene and Formatting
3. Infrastructure and Technical Configuration
4. Recipient List Management
5. Engagement and Complaint Monitoring
6. Summary Recommendations
- Align headers and domains with clear, professional identities.
- Respect opt-in and unsubscribe behaviors with transparent mechanisms.
- Structure content to be clean, concise, and free of deceptive or spammy characteristics.
- Maintain technical hygiene through DNS, TLS, SPF limits, and ARC usage.
- Monitor sender reputation and user engagement continuously.
- Ensure SPF and DKIM are properly configured and aligned with the domain in the
Fromp=none.
Immediate Impact and Risks of Non - compliance
As of May 2025, domains that fail SPF or DKIM checks or lack a correctly configured DMARC policy with alignment will risk having their emails marked as spam or not delivered at all. Misalignment occurs when the domain used in the message's "From" address doesn't match the domains authenticated by SPF or DKIM.
Organizations failing to comply face significant risks, including diminished deliverability rates, compromised customer trust, and increased susceptibility to impersonation attacks. These impacts directly affect an organization's reputation, customer engagement, and potentially, its revenue.
Actionable Recommendations for Immediate Implementation
To effectively prepare for these mandatory standards, organizations should:
- Audit current DNS records: Utilize tools such as "dig" or Google DNS to verify SPF, DKIM, and DMARC records.
- Begin with Monitoring (p=none): Initially deploy DMARC in monitoring mode to understand email flows and detect anomalies without risking legitimate email delivery.
- Gradually enforce stricter policies: Move from quarantine to full rejection while monitoring.
- Ensure domain alignment: "From" domain must match what’s authenticated via SPF or DKIM.
- Maintain email hygiene: Clean lists, include a clear opt-out option, and avoid using misleading subject lines or headers.
Start Your DMARC Journey with CTM360 Free Community Edition
To support organizations navigating these changes, CTM360 offers a complimentary zero-cost Community Edition platform. It allows comprehensive monitoring, management, and enhancement of your DMARC records and email authentication setup. This proactive approach helps organizations reduce risks associated with impersonation attacks and maintain reliable email communication.
Join CTM360 Community Edition today, no hidden costs, simply real security.
Reference:
Disclaimer:
The information contained in this document is meant to provide general guidance and brief information to the intended recipient pertaining to the incident and recommended action. Therefore, this information is provided "as is" without warranties of any kind, express or implied, including accuracy, timeliness, and completeness.
Consequently, under NO condition shall CTM360®, its related partners, directors, principals, agents, or employees be liable for any direct, indirect, accidental, special, exemplary, punitive, consequential, or other damages or claims whatsoever including, but not limited to loss of data, loss in profits/business, network disruption...etc., arisina out of or in connection with this advisory.
For more information: Email: monitor@ctm360.com Tel: (973) 77 360 360